Accelerating MES Time to Value Through Micro Wins and Low-Risk Pilots
Accelerating MES Time to Value Through Micro Wins and Low-Risk Pilots
In our deployment experience, long MES programs stall when project scope expands faster than operational learning. This risk frequently manifests as missed deadlines and costly software rework.
A study of large enterprise IT projects revealed that 1 in 6 experienced average cost overruns of 200%. Achieving a fast MES implementation requires structuring rollout phases so every step yields verifiable proof rather than endless configuration.
"MES time to value typically improves when you prove value in small, controlled steps."
Micro wins and low-risk pilots establish early momentum while managing uncertainty on the shop floor. A cloud architecture shortens initial setup, but cloud capability alone cannot resolve ambiguous goals or messy master data.
Rapid deployment succeeds when you define value using clear operational metrics, focus on targeted workflows operators adoption requires, and treat your initial pilot as a controlled production release.
Define MES time to value and realistic benchmark ranges
MES time to value measures the elapsed time from project kickoff to the first verified operational outcome recognized by plant leadership.
This milestone must reflect a measurable operational change rather than a software demonstration. Setting a single primary outcome accelerates deployment schedules while keeping secondary objectives from expanding project scope.
We recommend tracking two distinct project milestones: first value and sustained value. First value occurs when the system operates on a live line with active users, generating trusted data for a targeted process.
Sustained value is reached when that process executes reliably across all shifts, feeding structured data to process owners without requiring daily intervention.
In tightly scoped pilots, cloud MES time to value is often measured in weeks rather than quarters when customization and integration complexity remain limited.
Initial deployment phases should focus on setting up core master data, configuring a single workflow, training key users, and running controlled production.
Timelines naturally extend when adding full ERP write-backs, complex machinery interfaces, or specialized validation documentation. Use benchmark ranges as planning guardrails while managing directly to operational results.
Identify micro wins that reduce risk and prove value
Micro wins are focused workflow updates that improve operational control or visibility without forcing a full system rollout.
The most effective micro wins alter operator behavior in ways leadership can measure within just a few shifts.
We see teams achieve rapid results by focusing on changes that reduce scrap rates, eliminate manual part lookups, or prevent out-of-sequence processing.
Selecting the right micro wins often has more impact on MES time to value than adding complex features.
- Capture cycle start and stop events to generate accurate takt time data.
- Require barcode scans at workstations to verify correct material at point-of-use.
- Enforce automated routing rules that block units from advancing out of sequence.
- Standardize defect codes and repair entry to yield actionable quality reports.
- Deploy electronic work instructions with automated version control and sign-off.
Prioritize use cases based on daily line friction and user adoption rather than internal politics. A micro win that prevents a single quality escape delivers far more value than an intricate dashboard line leads ignore.
Keep changes localized to one work cell initially, while structuring data fields to support enterprise-wide scalability.
Scope a low-risk pilot with clear success criteria
A low-risk pilot is a production-grade deployment with limited operational scope, controlled change windows, and explicit exit criteria.
It utilizes live production units, standard shift operators, and real shop floor conditions so deployment data remains fully credible. Project risk decreases when a pilot assigns a single process owner, targets one core workflow, and follows a structured cutover plan.
Consider a medical device assembly line piloting component serialization and route enforcement for a single product family across three stations.
The integration receives work orders from ERP via a read-only data feed, utilizes handheld scanners at each work cell, and requires defect logs before final packout.
Operators execute production under the new system for two weeks while supervisors review process exceptions daily.
Defining exit criteria upfront protects project velocity by preventing uncontrolled scope expansion.
The pilot meets success criteria when line throughput hits target benchmarks, system exceptions fall within acceptable tolerances, and electronic device history records match physical travelers during audit checks.
Common stop conditions include unstable master data, poor scan compliance, or excessive manual overrides. Lock core requirements during the pilot window, batching non-critical updates into subsequent stabilization sprints.
Prepare data, integrations, and roles before configuration starts
Fast MES implementation depends more on operational readiness than on configuration speed.
Master data must be cleaned and validated before go-live to prevent production stops. System integration boundaries must be established early so engineering teams avoid mid-sprint configuration changes.
Clear operational roles are essential because dedicated owners must govern routings, electronic work instructions, and process exceptions from day one.
Interoperability issues generate substantial financial losses across manufacturing projects. A study by the National Institute of Standards and Technology estimated that inadequate software interoperability cost the U.S. capital facilities industry $15.8 billion annually.
Unclear data ownership and ambiguous system handoffs bleed project time.
Treating master data as a core deliverable prevents costly integration delays during rollout.
Assign explicit ownership roles prior to system configuration. Designate one lead to approve routings and revision controls, one owner to manage defect code governance, and an integration lead to maintain the ERP interface contract.
Establish a written escalation protocol for line stops tied to software issues so downtime decisions are resolved immediately rather than waiting for weekly steering committee reviews.
Use cloud deployment patterns that shorten implementation cycles
Cloud deployment shortens implementation cycles when engineering teams standardize how changes are built, tested, and released.
The most effective deployment pattern prioritizes standard software configuration first, system integrations second, and custom modifications last. Project velocity increases when every development sprint produces a stable, deployable increment.
Maintain a consistent promotion path from staging environments to production, managing configuration updates under strict revision control.
A multi-tenant cloud MES like 42Q supports rapid deployment because updates and access controls are managed within a unified cloud service.
Multi-tenant cloud architecture enables deployment teams to reset test data, rehearse cutovers, and update user permissions without waiting on server infrastructure provisioning.
Tradeoffs exist around regulatory compliance and internal security reviews. Identity management, comprehensive audit trails, and electronic signatures must be treated as mandatory baseline requirements.
Schedule network security reviews early in the project timeline to ensure access permissions and data flows receive approval before configuration completes.
Track leading metrics to manage rollout speed and quality
Leading metrics keep rapid MES deployment on schedule by monitoring user adoption and data quality before financial outcomes register.
Project leads gain actionable insights by tracking daily operator compliance rates, system override volumes, and interface stability. Monitoring a focused set of leading indicators is far more effective than reviewing complex dashboards.
| Checkpoint | What good looks like in plain terms |
| Operator compliance rate | Most units follow the intended workflow without workarounds. |
| Exception and override volume | Overrides are rare and reviewed with a clear reason code. |
| Master data change frequency | Routings and instructions stay stable during the pilot window. |
| Interface reliability | Work orders and confirmations flow on schedule without manual reentry. |
| Support readiness | Shift leads can resolve common issues using agreed runbooks. |
Monitoring daily operator compliance enables project leads to correct workflow friction before expanding scope.
Use metrics to trigger immediate operational corrections. A drop in operator compliance should trigger floor coaching and screen layout adjustments rather than generic training presentations.
A spike in manual overrides should prompt a temporary configuration freeze and structured root-cause analysis. When leading metrics remain stable for several consecutive weeks, the project team has earned the right to expand scope.
Scale from pilot to plants with repeatable templates
Scaling MES capability across plants succeeds when pilot outputs are converted into standardized, repeatable templates.
Deployment templates should encompass master data standards, role permissions, work instruction templates, and release checklists. Momentum builds when every new manufacturing line builds upon an established baseline, modifying only plant-specific parameters.
"Stick with micro wins as the unit of progress and treat scope increases as earned, not assumed."
Expand in controlled deployment waves that align with your site support capacity. Each rollout wave should introduce a limited number of production lines, reserving dedicated capacity for stabilization and operator feedback.
Maintain strict compliance thresholds, refusing to expand deployment to new lines if data quality drops below pilot benchmarks.
Scaling in controlled deployment waves protects release discipline and prevents operational disruption across sites.
Standardization requires discipline initially, but it significantly accelerates subsequent multi-plant rollouts.
Resist executive pressure to execute a full-scale simultaneous deployment before operational templates are proven. Teams running cloud MES initiatives, including those deploying 42Q, succeed when they treat release discipline, data ownership, and operator adoption as non-negotiable standards.
Ready to accelerate your deployment timeline?
See how low-risk pilots and cloud architecture shorten time to value without putting shop floor output at risk. Request a demo of 42Q to evaluate automated routing controls and cloud deployment templates for your operations.
Key Takeaways:
- MES time to value improves when you define first value as a verified operational outcome, then protect scope so learning stays ahead of configuration.
- Micro wins and low risk pilots work when they change operator behavior with measurable compliance, exceptions, and data quality targets.
- Scaling across lines and plants is more likely to succeed when templates, data ownership, and release discipline stay consistent across every rollout wave.
Manufacturing Transformation Roadmap and Governance Scorecard
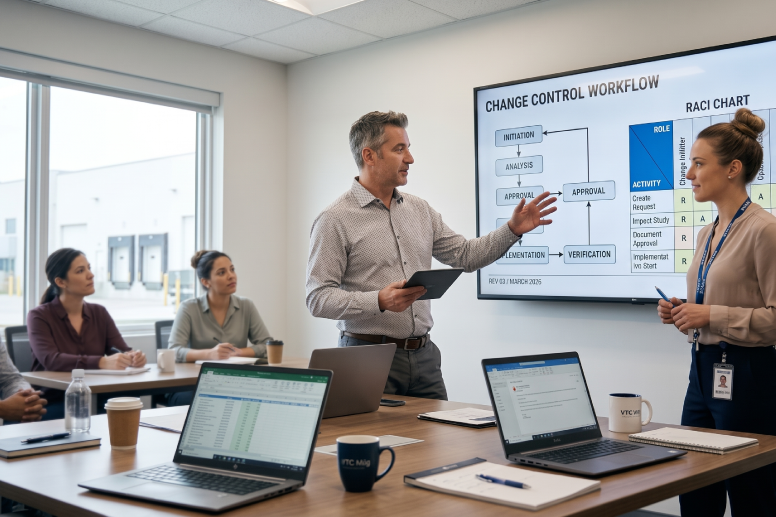
Manufacturing Transformation Roadmap and Governance Scorecard
"A manufacturing roadmap only works when governance and KPIs come first."
In our deployment experience, plants do not lose money because they lack strategic ideas. They lose money because priorities, standards, and accountability remain fuzzy when execution gets difficult.
Cost of poor quality commonly reaches 15% to 20% of sales revenue. This makes scrap, rework, and customer returns a direct margin issue rather than a minor shop floor problem.
A practical transformation roadmap ties every workstream directly back to financial outcomes, customer commitments, and audit readiness.
MES and connected operations raise the bar for execution consistency across global plants and product lines. A maturity model provides realistic sequencing so you do not install systems faster than your teams can adopt them.
Governance keeps sites aligned when local constraints and plant preferences collide. A structured KPI scorecard closes the loop so leadership can fund proven initiatives and retire underperforming workflows.
Define business outcomes and constraints for a factory roadmap
A factory roadmap establishes the specific operational outcomes that directly drive P&L performance and customer scorecards.
We recommend writing targets in plain language, such as cutting scrap, improving on-time delivery, or reducing lead time variance.
Constraints must be evaluated alongside targeted outcomes so deployment plans remain executable across all manufacturing facilities.
Start with three to five measurable outcomes that finance and operations leadership both accept, then identify the operational levers that influence them.
Scrap and rework point directly to defect capture, repair loops, and controlled work instructions. On-time delivery relies on dispatch discipline, real-time WIP visibility, and realistic cycle time standards. Customer audits require complete traceability and controlled document revisions.
Clear business outcomes protect operating margins, while explicit constraints preserve schedule credibility and executive trust.
Treat operational constraints as core design inputs rather than unexpected barriers. Regulatory validation windows, cybersecurity policies, IT staffing, and server management rules shape deployment velocity.
Product mix and routing complexity dictate where standard templates work and where plant-specific parameters are required.
Use a manufacturing maturity model to sequence capabilities and sites
A manufacturing maturity model sequences plant capabilities so each phase builds operational discipline before adding scope.
Early stages focus on paperless execution and basic traceability. Later stages shift to real-time performance management like OEE and SPC, followed by advanced optimization.
Site sequencing follows the same logic, starting where process stability supports a repeatable rollout.
Pick one enterprise maturity path and publish clear completion criteria for each stage, including process ownership and data definitions.
We frequently see teams fall into the trap of mixing advanced analytics with weak transaction discipline, producing dashboards that line supervisors do not trust.
Establishing a clear maturity model prevents premature rollouts and sets realistic expectations for shop floor teams.
This approach also supports supervisors during deployment transitions, ensuring teams are not overwhelmed by new administrative tasks without added resources.
| Roadmap checkpoint | What it confirms and why it matters |
| Paperless execution readiness | Work instructions and approvals follow a controlled revision process. |
| Traceability and genealogy scope | Serialization rules match customer contracts and audit needs. |
| WIP visibility definition | WIP states are consistent across plants and product families. |
| Performance management setup | Loss codes are standardized so OEE comparisons stay meaningful. |
| Optimization entry criteria | Core transactions are reliable enough to support higher-level analysis. |
Pick high value use cases before platform and data work
Selecting high-value use cases prior to platform selection defines project scope, data requirements, and necessary system integrations.
High-value use cases have clear business owners, defined process boundaries, and direct impact on operating margin, delivery performance, or product quality.
Funding and staffing remain steady when every technical deployment task maps directly to an operational outcome.
Project waste accumulates rapidly when teams deploy software features without a prioritized operational backlog. Poor project management wastes an average of 9.4% of every dollar invested, impacting capital efficiency.
Use-case selection must also account for customer risk, especially when late shipments or traceability gaps threaten contract renewals.
Linking every technical task directly to an operational outcome keeps project funding steady and protects executive sponsorship.
We recommend following these five criteria when selecting initial use cases:
- Link the use case directly to one financial metric and one customer service metric.
- Confirm a single process owner with authority to approve standardized workflows.
- Limit the initial release to one product family or one primary routing pattern.
- Specify required system integrations, including ERP, automated test, or machine data.
- Define completion criteria using clear KPIs and audit-ready electronic records.
Set digital factory governance for roles, standards, and change control
Digital factory governance establishes clear authorization rules, change review procedures, and standardized execution controls across facilities.
Governance roles must separate process ownership from technical system configuration so accountability remains clear.
Change control must cover master data, electronic work instructions, routing definitions, and reporting metrics so performance comparisons remain valid over time.
Start with a compact governance core consisting of operations, quality, IT, and plant leadership. Publish a practical RACI matrix that supervisors can execute during a shift change.
Standards should be established at a level that prevents operational drift, including naming conventions for routings, defect codes, and equipment identifiers.
Establishing unified definitions for scrap, rework, and good units protects financial reporting accuracy across plants.
Release notes must detail process impacts, training requirements, and document updates. Without structured change control, operators rely on undocumented expertise, leading to quality variation.
When governance is firm yet practical, individual plants maintain operational execution flexibility while sharing a standardized system language across the enterprise.
Run multi-plant MES governance for configuration releases and master data
Multi-plant MES governance aligns software configuration, master data, and system releases so every plant executes identical business logic while respecting local constraints.
Separating global templates from plant-specific parameters enables central control while allowing controlled local execution.
This separation reduces rework and protects key metric integrity across your manufacturing network.
Consider an engineering update adding a torque verification step. Engineering updates the routing and work instruction, Quality adds a defect code, and the line connects a smart torque tool.
A controlled release deploys the update to Plant A and Plant B simultaneously. Plant C delays execution by one week to align with local tool calibration schedules without breaking validation rules.
A cloud execution layer like 42Q supports centralized templates while providing site-level configuration controls.
Release governance must also define rollback protocols, data migration rules, and reporting update schedules to prevent discrepancies between plant performance and financial reports.
As covered in our Cloud vs. On-Prem guide, central cloud architecture enables enterprise-grade security standards without site-by-site server management overhead. Master data stewardship becomes an ongoing operating discipline.
Create an MES KPI scorecard for finance, service, and quality
An MES KPI scorecard connects shop floor execution metrics directly to high-level financial and operational benchmarks.
A balanced scorecard pairs service metrics like schedule adherence with quality indicators like first-pass yield and genealogy completeness. Each KPI requires an assigned owner, a clear formula, and a reliable data refresh schedule.
"The scorecard becomes your operating contract across plants, especially when product lines share customers and partner commitments."
Start with a focused set of KPIs spanning finance, service, and quality, ensuring every metric triggers a defined operational response.
If first-pass yield drops, teams initiate defect Pareto reviews or work instruction updates rather than creating additional dashboards. If cycle time variance increases, supervisors focus on dispatch discipline and routing accuracy.
Treating an MES KPI scorecard as an active management system rather than a static reporting layer protects operating margin.
As detailed in our MES business case analysis, unifying performance metrics across facilities prevents reporting discrepancies during leadership reviews.
Teams deploying platforms like 42Q succeed by enforcing strict master data ownership and change control, keeping their transformation roadmap tied to measurable business outcomes.
Ready to build your manufacturing transformation roadmap?
See how cloud MES simplifies multi-plant governance and automated KPI reporting. Request a demo of 42Q governance controls to evaluate your digital manufacturing strategy.
Key Takeaways:
- Start with measurable business outcomes and explicit constraints so every roadmap task ties back to margin, service, and audit commitments.
- Use a maturity model to sequence capabilities and site rollouts, keeping standards and operating discipline ahead of advanced reporting and analytics.
- Run multi-plant MES with clear governance and a stable KPI scorecard so changes, master data, and performance comparisons stay consistent across sites.
Medical Manufacturing Traceability and Electronic Device History Records
Medical Manufacturing Traceability and Electronic Device History Records
A reliable Electronic Device History Record (eDHR) provides verifiable proof of every step in a device's manufacturing journey.
This proof carries a long shelf life. FDA quality system regulations require maintaining device records for at least two years from the date of release or for the expected life of the device, whichever is longer.
If your traceability relies on spreadsheets, shared drives, or manual reconciliation, you will experience release delays, audit friction, and revenue bottlenecks.
In our deployment experience, the stronger approach treats eDHR in medical manufacturing as an active execution system rather than a passive filing cabinet.
"The stronger approach treats eDHR medical manufacturing as an execution system, not a filing system."
By capturing mandatory data at each station and connecting it to real-time lot genealogy, you simplify investigations, speed up disposition decisions, and protect operating margins.
Define electronic device history records and required manufacturing data
An electronic device history record defines the complete, time-ordered evidence of how a specific unit, lot, or batch was manufactured and accepted.
It links unit identity, routing steps, component consumption, test results, deviations, and release approvals into a single audit-ready dataset.
To build a functional eDHR, engineering and quality teams must separate release-critical data from secondary operational metrics.
Release-critical data includes what was built, what components were consumed, where it was built, who performed each step, and which specifications passed.
You also need automated links to controlled documents like electronic work instructions and inspection plans, proving active revisions at execution.
Defining clear eDHR parameters enables medical device manufacturers to pass audits and release products without manual data assembly.
| What must be traceable | Why it matters during audits and investigations | What to control in your eDHR process |
| Unit, lot, and serial identity | Limits the scope of holds and recalls to affected product | Unique identifiers with scan-based capture at each key step |
| Material and component consumption | Connects defects to supplier lots and internal inventory movements | Lot-controlled issues and controlled substitutions with approvals |
| Routing and step completion evidence | Shows required steps were performed in the intended order | Route controls with timestamps, operators, and stations recorded |
| Test and inspection results | Supports release and explains why nonconforming product was stopped | Result capture with limits, pass fail rules, and record locking |
| Deviations and disposition records | Proves your response was controlled and risk-based | Link deviations to affected units and require approvals to proceed |
| Release approvals and signatures | Demonstrates accountability for shipment readiness | Electronic signatures with roles, meaning, and audit trails |
Map product and lot genealogy from materials through shipment
Mapping product and lot genealogy requires establishing a continuous, bi-directional record chain from incoming raw materials through final device shipment.
Genealogy models must account for complex production relationships, including lot splits, panelization, batch merges, and component replacements.
When genealogy chains break, quality investigations expand far beyond the affected lot, increasing scrap costs and holding up valid inventory.
Map your genealogy structure alongside physical material flow. Identify key points where unit identity changes, such as kitting, sterilization, packaging, and relabeling.
Continuous lot genealogy enables precise containment of suspect components, protecting non-affected inventory from unnecessary holds.
Establishing clear genealogy across enterprise software prevents data silos. Receiving events typically start in ERP, while execution occurs on the shop floor and quality events live in QMS.
Without automated system links, responding to supplier defects becomes slow and labor-intensive. A connected genealogy model shrinks the time from problem discovery to target containment.
Set up eDHR workflows that match your manufacturing routes
Setting up compliant eDHR workflows requires translating physical routing steps directly into automated data entry checkpoints in MES.
Each routing step requires defined entry prerequisites, expected process outputs, and mandatory acceptance criteria.
When workflow controls match actual line execution, the eDHR generates automatically as a byproduct of production.
Build your digital workflow around simple, repeatable operator controls. Line staff need clear station status, minimal manual data entry, and scan-based inputs.
Designing eDHR workflows that mirror actual shop floor routines enables fast adoption and prevents data entry workarounds.
Quality teams require defined decision logic within the workflow, enforcing holds when test limits fail or deviations occur.
Engineering teams benefit from revision-controlled routing steps, ensuring operators only execute against active, approved procedures. Matching workflows to physical routes reduces training time while supporting strict process compliance.
Maintain traceability across rework, repairs, and nonconforming events
Maintaining traceability during rework requires linking every nonconforming event, component swap, and re-test result directly back to the primary unit serial.
"Rework and repair are where traceability often fails because identity, configuration, and acceptance criteria can change midstream."
If repair loops operate outside the main MES, configuration drift occurs and device history records become incomplete.
A compliant repair loop follows a structured path on the shop floor. When a serialized unit fails functional testing, the system logs the failure code and locks the unit from progressing to packout.
A nonconformance record opens automatically, linking the defect code directly to that unit's history.
Enforcing automated repair loops prevents unapproved rework and ensures component substitutions are fully documented in the eDHR.
The technician records the replaced component lot number and the corrective action taken under approved engineering procedures.
The unit re-enters the routing at a mandatory re-test operation, attaching new verification results to the original serial record.
A quality engineer reviews and signs off on the disposition closeout, preserving complete history from original assembly through final release.
Control data integrity, access, and electronic signatures for audits
Controlling data integrity for audits requires role-based access, immutable system audit logs, and 21 CFR Part 11 compliant electronic signatures.
Auditors evaluate whether manufacturing data is trustworthy, traceable, and protected from unauthorized alterations.
Without secure system logs and clear signature meanings, an eDHR loses its value as defensible regulatory evidence.
Long-term data retention requirements reinforce the need for robust system controls. EU MDR regulations mandate keeping device documentation for at least 10 years after market placement, and 15 years for implantable devices.
Implementing role-based access controls and secure audit trails supports data integrity across long regulatory retention periods.
System signatures must capture who signed, what specific action was approved, and the exact timestamp of execution.
System change logs should capture original values, updated values, and the operational reason for change.
These controls support compliance controls for FDA 21 CFR Part 820 and ISO 13485 standards, replacing manual sign-offs with defensible electronic records.
Choose an MES that supports eDHR compliance at scale
Choosing an MES that supports eDHR compliance requires selecting a platform capable of enforcing route controls, managing complex genealogy, and scaling across facilities without custom code.
The software must support process controls while simplifying data retrieval during regulatory audits.
We recommend evaluating MES platforms against these core eDHR criteria:
- Provides end-to-end genealogy that manages splits, merges, and component substitutions.
- Supports controlled work instructions and revision-effective routing changes.
- Captures test results and signatures with immutable, time-stamped audit trails.
- Connects cleanly to ERP and equipment interfaces without manual data entry.
- Scales across multiple manufacturing plants with standardized master data models.
Operational constraints vary across sites, including network connectivity, device interfaces, and validation protocols.
As covered in our Cloud vs. On-Prem guide, a cloud MES platform like 42Q enables multi-plant visibility and standardized eDHR controls.
As discussed in our Business Case analysis, centralizing eDHR management removes server management overhead while supporting enterprise-grade security standards.
Avoid common traceability gaps that delay releases and revenue
Avoiding common traceability gaps requires eliminating undocumented expertise, enforcing mandatory data capture before step completion, and unifying deviation records within the eDHR.
Traceability failures rarely result from lack of effort. They stem from fragmented systems and manual record assembly.
The most critical gaps occur when serial numbers change without recorded relationships or when deviations are filed in separate systems.
Address these risks by assigning clear ownership for master data definitions, lot structure rules, and release criteria.
Enforcing data completeness checks before release enables medical manufacturers to ship products faster and reduce inventory hold times.
Training must align directly with the digital workflows operators execute on the floor.
When you build traceability into daily manufacturing operations, product releases accelerate because the supporting evidence is complete, searchable, and audit-ready.
Teams running MES platforms like 42Q succeed by maintaining operational discipline and treating data integrity as a strategic production asset.
Ready to simplify your eDHR compliance?
See how automated eDHR and lot genealogy work in practice. Request a demo of eDHR compliance controls in 42Q to see how we enable audit-ready traceability.
Key Takeaways:
- Build the electronic device history record as work happens, with clear checkpoints tied to routing, so release decisions rely on complete evidence instead of late reconciliation that slows shipments and revenue.
- Keep lot genealogy continuous through splits, merges, substitutions, and rework, so investigations stay tightly scoped and customer and partner responses move faster.
- Pair MES controls with strong data integrity practices, including role-based access, clear electronic signature meaning, and consistent master data ownership, so records remain defensible across plants and long retention periods.
Modernizing Brownfield Factories without Disrupting Production
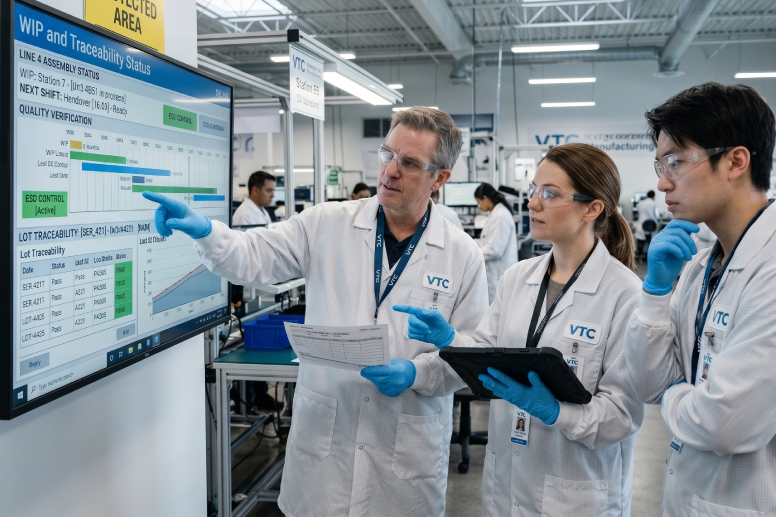
Modernizing Brownfield Factories without Disrupting Production
Modernizing a brownfield factory without downtime means layering digital execution on top of what already runs. Your lines already ship products and protect revenue. Modernization must respect uptime as a strict business constraint.
Manufacturing employs a large workforce you cannot pause and retrain all at once. U.S. manufacturing employment averages 12.9 million in 2024. That scale is exactly why a phased approach outperforms full-scale simultaneous deployment.
The goal is better control of quality, traceability, and flow while production continues. In our deployment experience, the most reliable path is disciplined sequencing. Start with a focused set of data that moves the needle.
Connect what you can from legacy equipment without rewiring the plant. Expand only when the line teams trust the system. Cloud MES enables this approach, provided you design for latency and security from day one.
Modernize brownfield factories by layering digital systems over operations
Brownfield modernization succeeds when you add new digital layers that sit alongside existing control and production routines. Start with basic visibility and traceability before adding tighter execution controls.
Keep the PLCs, HMIs, and proven work methods running while you digitize the record of what happened. This approach targets a direct reduction in risk to shipments and customer commitments. A layered model separates machine control, operator execution, and business reporting.
Each part can improve on its own schedule. You will typically keep machine control local, add MES for WIP tracking, and finally connect upstream systems for planning. This sequencing matters because brownfield factories carry years of local tweaks that keep yield stable.
A careful layer retains those hard-won gains while standardizing how production data is captured and reviewed. This also shifts how you staff modernization. As detailed in our Business Case guide, the financial impact surfaces quickly through fewer expedite cycles and cleaner data handoffs.
Prioritize use cases that raise throughput, quality, and on-time delivery
Prioritize modernization use cases based on measurable impacts to throughput, quality, and on-time delivery, rather than integration simplicity. Tie each use case to a specific constraint you already experience, such as a 45-minute changeover or delayed defect containment.
Start with what supervisors and quality engineers will use every day to build confidence and protect revenue. Use a short set of selection checks to keep scope tight. The goal is a release that operators accept and leadership can fund.
We recommend focusing on these practical checks for brownfield environments:
- Revenue impact is clearly linked to customer ship dates.
- Quality risk is reduced through improved genealogy tracking.
- Data exists or can be captured without intrusive machine changes.
- Operators can adopt the workflow inside normal shift routines.
- Integration effort stays bounded with a defined fallback plan.
Once priorities are clear, keep the first wave narrow. Limit the initial rollout to one product family. Process owners can validate data and adjust work instructions without constant exceptions. Expand only after you see stable usage.
Connect legacy equipment to MES using gateways, tags, and standards
Legacy equipment connects to MES successfully when you treat data capture as an engineering task with strict test criteria. Start with signals that matter for execution, like cycle start, good count, and key process parameters.
Use edge gateways and tag mapping to avoid rewriting underlying machine logic. The scope stays manageable when you define exactly what the MES needs and what the machine can reliably provide. A practical pattern on older equipment involves reading discrete signals and publishing time-stamped events to MES.
The machine program stays unchanged. Operators continue running the same start buttons, but they also scan work orders at the station. This enables the MES to link machine events to specific unit history without disrupting the operator's rhythm.
Safety and change control must sit beside connectivity work. Lockout and verification steps protect both people and production quality. Compliance matters because OSHA estimates lockout protocols prevent 120 fatalities and 50,000 injuries each year. A tight test plan keeps the line stable.
Assess cloud MES fit for security, latency, and plant connectivity
Assessing Cloud MES fitness requires verifying that your plant network can maintain connectivity and that security meets enterprise-grade standards. Security, latency, and identity controls must align with your specific regulatory and customer obligations.
The MES should support a clear integration path to ERP systems without requiring custom, one-off logic. Cloud adoption becomes highly practical when you treat the plant network and edge components as part of the MES design.
Teams often pair cloud MES with local gateways and store-and-forward buffering. The line keeps running even if network connectivity drops. Execution teams also need clear data residency and access controls to satisfy customer audits.
Cloud MES platforms like 42Q typically fit best when IT and OT share joint ownership for server management, user access, and patch cadence.
| Checkpoint | What you verify before rollout expands |
| Plant connectivity stability | Line teams can operate through routine network drops with buffered data. |
| Latency tolerance for execution steps | Operator scans and confirmations complete fast enough for takt time. |
| Security and access control model | User roles, audit logs, and authentication meet enterprise-grade standards. |
| Integration approach to ERP and quality | Interfaces have clear owners, version control, and test data sets. |
| Local support and operating model | OT and IT agree on monitoring, incident response, and change approvals. |
Sequence data, workflows, and user adoption to prevent production disruptions
Preventing disruption requires a phased sequence where data capture is stabilized before strict workflow enforcement begins. Start with passive visibility, add operator workflows, and then implement tighter routing controls after exceptions are fully understood.
Plan cutovers around shift patterns and product mix rather than arbitrary calendar milestones. Data comes first because it reveals where your current process deviates from instructions. Workflow follows closely behind.
Operators need a simple, repeatable path to record scrap and rework without slowing the line. An example is replacing paper logs with simple barcode scans for defect entry. Adoption happens last. People change behavior when supervisors and maintenance teams use the same digital record to solve daily problems.
Keep paper and digital systems running in parallel only long enough to validate, then retire the duplicate process to avoid confusion. Build training around shift turnover, common defects, and missing scan recovery.
Avoid integration failures in data governance, validation, and change control
Avoiding integration failures requires strict data governance, active validation routines, and tight change control. Most modernization failures stem from undocumented expertise and uncontrolled changes, not from the MES feature set.
Assign direct owners for every critical data element, including equipment tags, routing steps, and defect codes. Governance starts with definitions that remain consistent across plants and shifts. Agree on what counts as a good unit, what defines downtime, and who can edit history.
Validation requires comparing MES results to manual counts, quality records, and shipping data until variances are understood. Change control must include versioned work instructions and a rollback plan that production leaders accept.
This is where seasoned practitioner experience matters. As a division of Sanmina, 42Q operates across multiple factories and has seen that disciplined governance keeps modernization stable. Plants that do this improve consistency without gambling revenue on a full-scale simultaneous deployment.
Ready to connect your legacy equipment?
See exactly how edge connectivity works in practice. Request a demo of legacy equipment integration with 42Q to see how we enable seamless data capture without stopping production.
Key Takeaways:
- Brownfield modernization works best when digital execution gets layered onto existing operations, so you improve traceability and control without putting shipments at risk.
- Use case selection should start with throughput, quality, and on-time delivery outcomes, then narrow scope to what can be captured and adopted inside normal shift routines.
- Cloud MES and legacy integration succeed when connectivity, data governance, validation, and change control are treated as production disciplines, not IT tasks.
How to Standardize Manufacturing Workflows Across Global Plants
How to Standardize Manufacturing Workflows Across Global Plants
Standardized manufacturing workflows target a direct reduction in the scrap, rework, and late shipments that erode operating margins.
When the same product runs in multiple facilities, minor operational differences turn into real cost. A different torque spec, a missing inspection step, or an outdated instruction revision can show up as yield loss and customer complaints.
Cost of poor quality often reaches 15% to 20% of sales revenue, so tightening execution across sites has a direct impact on profitability.
In our deployment experience, the hard part isn’t writing a standard. The real challenge is translating that standard into routings, data collection, training, and approvals that operators can follow during a shift change on a busy line.
MES serves as the practical layer that enables process control at scale, provided you standardize critical execution gates while allowing room for valid plant constraints.
Standardized manufacturing workflows and what must stay consistent
Standardized manufacturing workflows mean the same product follows required steps, checks, and data capture protocols across every plant.
Facilities do not need identical equipment brands or identical screen layouts. However, plant leadership must maintain consistent routing intent, quality gates, and genealogy data so performance compares cleanly across sites.
Consistency must start where process variation carries the highest financial and quality risk. This includes product genealogy, critical-to-quality measurements, defect codes, and approval logic around holds and releases.
When these elements differ by site, organizations experience cross-plant yield debates and delayed containment. As covered in our business case analysis, unifying these execution standards removes shadow processes while protecting plant throughput.
Plant leaders still require flexibility for local execution. Shift patterns, labor skill levels, language preferences, and tooling vary by region. The goal is a stable core process definition paired with controlled options for local execution.
Select the global standards that matter for process control
Global MES standardization works when engineering teams focus on standards that directly affect product quality and release decisions.
Initial standardization efforts should establish rules for what operations are permitted, what parameters require recording, and what approvals must occur before a unit progresses. Additional features can roll out in subsequent phases.
Focus first on standards that turn ambiguity into clear binary pass or fail outcomes. Examples include required operations per product revision, automated data entry for IPC compliance testing, required test result limits, serialization formats, and defect handling paths.
A global template also requires a shared data dictionary across all locations. Terms like "rework," "repair," and "scrap" must share identical definitions when Finance and Quality review performance across plants.
If a process variation alters a release decision or prevents multi-plant reporting, it belongs in the global standard. If a difference only changes how a task runs on local machinery, treat it as a controlled plant option.
| What to standardize | What can vary by plant | What you risk if it varies |
| Routing sequence and required operations per product revision | Station layout and operator assignment within the same operation | Units skip steps and defects surface at customer inspection |
| Hold and release rules tied to quality and test outcomes | Who reviews the hold within an approved role structure | Different pass criteria and inconsistent lot disposition |
| Traceability fields like serial, lot, and component genealogy | Scan device type and local data entry ergonomics | Slow containment and incomplete recall readiness |
| Defect codes and repair loop requirements | Local repair bench tooling and work cell scheduling | Rework cost can’t be compared and root cause stays unclear |
| Work instruction revision control and acknowledgment capture | Language, images, and formatting suited to the workforce | Wrong revision used and audit trails become weak |
Design routings, route enforcement, and hold points in MES
Route enforcement in MES relies on system logic that blocks unit progression when required steps or tests remain incomplete.
Effective system design uses routings to set required operational order, validations to confirm unit identity, and hold points to pause flow when results demand review. This enforcement model maintains target process control without depending on operator memory.
Consider a serialized electronics assembly line running surface-mount, automated optical inspection, functional test, and packout. The system scans each unit at every station, checking that prior operations passed before opening the next work step.
A failed functional test routes the unit into a mandatory repair loop with specific defect codes, while a quality hold pauses packout until an authorized engineer inputs a release code.
Hold points define operational risk boundaries. If one plant can ship units following a soft test failure while another plant cannot, customers experience inconsistent product reliability. Route logic also needs clear paths for unexpected shop floor events. Power outages, line downtime, and partial rework happen during production. System routings must include approved paths for rework, scrap, and unit re-entry so WIP stays tracked inside the primary system.
Use electronic work instructions to align tasks and training
Electronic work instructions link the central engineering definition directly to the physical action an operator performs at a work cell.
A master routing may specify an adhesive application step, but final quality depends on details like mix ratios, bead patterns, cure times, and verification checks. Digital, revision-controlled instructions align execution and operator training across sites.
Standardized instructions support safety alongside quality. Workplace injuries and illnesses totaled 2.8 million in 2022, and outdated work instructions increase operational risk during shift changes and onboarding.
Digital instruction logs support compliance audits by capturing exact document revisions active during production, along with operator acknowledgments.
The primary challenge is balancing corporate control with local agility. Plant teams want to update work instructions quickly when replacing tools or addressing scrap, while corporate teams need change control to protect process integrity.
A structured approach uses global master templates with dedicated sections for local station equipment, while locking critical parameters at the product revision level.
Balance global templates with plant exceptions and governance
Balancing global templates with plant flexibility requires clear governance tiers rather than complex documentation.
Global templates define mandatory workflows, required data fields, and release approvals. Plant teams submit exception requests through a formal review process detailing the operational reason, assigned owner, and expiration date.
Governance models must operate fast enough to support production schedules. A change board meeting once a month cannot keep pace with component shortages or line disruptions, which encourages workarounds.
Establish structured change reviews for operational changes:
- Customer release criteria changes driven by updated inspection specs.
- Local station constraints requiring alternate operation order.
- Supplier packaging or component labeling variations altering material intake verification.
- Regional safety or environmental regulations affecting cell layout and tasks.
- Temporary process deviations with fixed expiration dates and defined lot disposition.
Minor setup changes can receive local engineering approval within pre-defined boundaries. Variations impacting compliance, product qualification, or customer specs require central review.
Roll out across sites with data, integrations, and change control
A multi-plant rollout relies on standardized master data and system integrations across all targeted facilities.
Deployment teams must define a single data model for parts, bills of materials, routings, and engineering revisions. Systems require reliable data exchange with enterprise ERP and automated test stations so shop floor execution matches financial records.
Select one lead facility and one product line to establish the global master template. Refine configuration, naming conventions, required genealogy fields, and routing standards before expanding to secondary plants.
Execution stalls when corporate teams define standards without providing site deployment resources. Using a cloud execution layer like 42Q enables multi-plant standard deployment without managing separate local server installations.
As detailed in our cloud strategy analysis, central cloud architecture allows corporate teams to publish standard routings while maintaining controlled configuration options for individual plants. Successful adoption still requires clear cutover milestones and hands-on shop floor support during initial go-live weeks.
Measure compliance, cycle time, and quality to sustain standards
Sustaining global standards requires continuous measurement of route compliance and quality metrics across every plant.
Engineering teams should monitor route compliance, hold rates, rework loops, and work instruction revisions, linking these signals to yield, escapes, and late shipments. A process standard without automated tracking degrades under peak production pressure.
Metrics must provide actionable feedback for plant supervisors, not just corporate dashboards.
Route compliance tracking highlights specific stations where operators frequently experience scanning errors, system delays, or unclear instructions. Cycle time tracking pinpoints approval bottlenecks that turn standard quality holds into production delays.
Global workflow standardization functions as an ongoing management system rather than a static IT setup. Organizations build long-term quality consistency by enforcing routings that match release logic, providing clear work instructions, and governing site variations systematically.
Manufacturing teams that run 42Q maintain stable quality controls while keeping individual facilities agile and productive.
Ready to standardize your global manufacturing workflows?
See how cloud MES enforces process control across plants without restricting local line agility. Request a demo of 42Q global route enforcement to evaluate automated routing controls for your operations.
Key Takeaways:
- Standardize the workflow elements that affect release decisions and traceability so quality, cost, and customer performance stay comparable across plants.
- Use MES routings, validations, and hold points to support consistent process control while still allowing controlled rework and approved exception paths.
- Keep standards alive with clear governance and ongoing measurement of route compliance, cycle time, and rework so plants don’t drift under schedule pressure.
Why Cloud MES Implementations Fail When Processes Are Not Standardized
Why Cloud MES Implementations Fail When Processes Are Not Standardized
In our deployment experience, cloud MES succeeds only after shop floor processes are standardized. When a project team attempts to "standardize inside the software" during launch, the effort degrades into a series of late-stage arguments, workarounds, and missed milestones.
A peer-reviewed healthcare study on a 19-step surgical checklist demonstrated that mortality dropped from 1.5% to 0.8% once teams executed the exact same steps every time. Manufacturing operations face similar operational mechanisms.
Cloud MES accelerates the visibility of process gaps because workflows, routes, and data rules get enforced consistently across shifts and sites. Standardizing shop floor processes prior to software deployment enables teams to achieve predictable data quality and fast time to value.
This alignment connects directly to the core financial metrics detailed in our MES Business Case guides, as downstream traceability and yield analytics depend entirely on stable input processes.
Process variation is a leading cause of MES rollout failure
Process variation breaks software execution by forcing the MES to handle endless informal exceptions instead of repeatable workflows. When operations lack standardized execution paths, project teams spend valuable engineering hours debating special cases rather than improving throughput.
Standardization does not mean every product must follow an identical manufacturing path. It requires your team to agree on a single best-known method for each operation, alongside governed rules for planned variants like rework or optional quality gates.
We see customers struggle when different shift supervisors approve conflicting routes or interpret quality rules differently. Locking down the standard happy path first eliminates the primary cause of operator friction during system adoption.
Reducing deployment risk begins with defining a short, approved list of controlled process exceptions. This foundation enables software configuration to reflect agreed-upon operational realities rather than undocumented shift habits.
Common MES implementation problems start with unclear work instructions
Unclear work instructions force operators to improvise, transforming the MES into a dispute resolver rather than an execution driver. When shop floor instructions are vague or outdated, operators adopt undocumented workarounds that break data integrity.
Consider a common assembly line scenario. An operator reads a paper document specifying 8 newton-meters of torque, while the workstation screen displays 6 newton-meters due to an unreleased engineering update.
The physical unit passes inspection, but the recorded system data conflicts with the actual method used. Linking digitally governed work instructions directly to automated routing steps prevents costly quality holds and audit exceptions.
Clear instructions require controlled revision management, visual clarity, and direct triggers within the routing sequence. If work instructions live in separate, unmanaged documents, your MES rollout will feel like an endless documentation project.
Decide when to change processes instead of customizing MES
Process changes should always take priority over software customization because custom code multiplies long-term support complexity and testing overhead. While custom coding can mimic messy legacy habits, it creates brittle integrations and delays future system updates.
Software errors carry substantial economic weight across manufacturing operations. A landmark government study estimated that software defects cost the U.S. economy $59.5 billion annually.
Heavily customized systems add excessive code paths that require validation every time you update or expand software functions. Choosing process standardization over custom software logic protects system agility and supports long-term platform maintainability.
| What You See During Rollout | What It Signals About the Process | What to Fix Before Adding Scope |
| Operators ask which step comes next | The routing is not a shared standard across shifts. | Agree on one routing per product family and freeze it. |
| Quality checks get skipped or duplicated | Inspection intent is unclear or disconnected from risk. | Define clear triggers for checks and required dispositions. |
| Data fields are treated as optional | Required data parameters are poorly defined at the point of work. | Set mandatory data fields per step and block completion if missing. |
| Rework becomes a shadow process | Rework routes and signoffs lack formal standardization. | Create controlled rework paths with explicit entry criteria. |
| Integrations break on part changes | Master data ownership and change control mechanisms are weak. | Assign clear data stewards and mandate field approval workflows. |
Evaluate customizations with a simple rule. If two plants execute the same operation differently due to habit, standardize the workflow and configure the software once. Reserve custom routing strictly for mandatory regulatory, safety, or unique equipment constraints.
Cloud MES configuration fails when routing rules are inconsistent
Inconsistent routing rules cause the MES to consistently enforce incorrect process sequences, leading to line halts and untrusted cycle time metrics. When routing definitions vary across lines, system automation triggers improper holds and generates manual override requests.
Routing standardization requires establishing clear definitions for entry states, exit conditions, pass and fail criteria, and rework diversions. Using different operational names for identical steps fragments enterprise reporting and prevents multi-plant benchmarking.
Establishing a standardized routing grammar across your facility network enables repeatable software configuration without constant re-interpretation.
Start by standardizing operation naming conventions across all shifts. Limit alternate routing options to explicit, approved operational reasons. Treat every manual system override as a process defect that requires root cause analysis and corrective action.
Standardize master data before mapping equipment and quality checks
Master data forms the structural foundation for every shop floor transaction, material movement, and quality record. If part numbers, bill of materials revisions, work centers, and defect codes vary between systems, integration mapping will fail.
Equipment connectivity and automated quality gates rely on matching identifiers across enterprise software layers. Standardizing core master data objects prior to integration builds a reliable foundation for automated device connectivity.
Focus initial governance on essential objects, including product identifiers, revision rules, routing codes, equipment IDs, and defect taxonomies. If ERP, PLM, and shop floor systems use conflicting naming conventions, integration interfaces constantly break during engineering changes.
Effective data governance relies on operational discipline rather than software features. Assign clear data owners, define allowed value ranges, and establish strict change windows for floor updates. This structure aligns directly with our core guidelines on Connected Manufacturing.
Start with a pilot process then scale across plants
A pilot deployment proves that your standardized shop floor baseline is executable, measurable, and repeatable before launching across additional facilities. Selecting a stable production line with clear acceptance criteria allows your team to validate routings and data collection without getting overwhelmed by exceptions.
The primary objective of a pilot is not a static demonstration. A successful pilot creates a reusable operational template that enables rapid scaling across plants with controlled local variation.
Formalize the routing, stabilize instruction formats, and lock the required data collection points per step. When expanding to subsequent lines or facilities, copy the baseline template and approve only justified variations, such as localized equipment constraints.
In our multi-site deployments, cloud platforms simplify this scaling pattern. Teams running 42Q utilize the first validated production line as an enterprise reference model, replicating proven configurations across global sites without executing full-scale simultaneous deployments.
Governance that keeps processes consistent after cloud MES go-live
Post-go-live governance prevents operational drift and stops shop floor teams from returning to unapproved manual workarounds. Without active process ownership, operators develop informal shortcuts and engineers push unreviewed routing updates that disrupt downstream analytics.
Governance enables continuous improvements to enhance operational standards rather than creating uncontrolled process variants. Active post-launch governance preserves process alignment and protects long-term MES value realization.
To maintain process consistency across shifts, implement these core operational safeguards:
- Assign a dedicated process owner per value stream with explicit authority to review change requests.
- Enforce a digital change control workflow that links software configuration updates directly to operator training.
- Maintain a single, centralized library for all routing definitions and instruction templates.
- Audit system overrides on a weekly cadence and treat unauthorized workarounds as process defects.
- Appoint master data stewards to enforce controlled naming conventions and revision rules.
Practical shop floor governance requires a short weekly review cadence and a clear protocol for elevating validated process improvements into new global standards. Software platforms support compliance controls, but sustainable success requires process ownership and master data control.
Ready to standardize your shop floor processes before rollout? Request our MES Process Standardization Audit Checklist to evaluate your routing and master data readiness, or schedule a demo to see how 42Q manages reusable process templates across plants.
Key Takeaways
- Standardize Before Software: Cloud MES will consistently enforce whatever variation exists on your shop floor, making process stabilization essential prior to software configuration.
- Focus on Core Process Inputs: Clear work instructions, locked routings, and governed master data eliminate execution friction faster than complex custom code.
- Prove and Replicate: Validate a repeatable process template through a single pilot line, then scale across plants using strict change control so exceptions do not become new norms.
Cloud MES Foundations for Scalable and Intelligent Manufacturing
Cloud MES Foundations for Scalable and Intelligent Manufacturing
In our deployment experience, cloud MES provides consistent execution control across plants with zero server infrastructure on-site. Manufacturing teams now expect cloud delivery for enterprise software, yet shop floors still require strict discipline around routing, quality, and traceability.
Cloud adoption is an operational norm across IT enterprise platforms. Eurostat reports that 45.2% of EU enterprises purchased cloud computing services, with adoption in advanced manufacturing sectors exceeding 70%.
Treating cloud MES as a continuous operational capability targets stable adoption and protects shop floor data integrity. This aligns directly with the financial framework in our MES Business Case guides, as speed to value relies on eliminating isolated plant hardware.
What is cloud MES and what problems it solves
Cloud MES is a cloud-delivered manufacturing execution system that standardizes, controls, and records production transactions in real time. It eliminates paper records, disconnected spreadsheets, and legacy plant systems that cause traceability gaps and unapproved process variations.
We see customers struggle when different plants manufacture the same product using inconsistent steps or logging defect codes differently. A cloud manufacturing platform closes execution gaps by enforcing mandatory data collection and controlled routings per unit.
The platform maintains single-unit genealogy, station-level transactions, routing rules, and nonconformance workflows. It supports ERP planning without replacing it, enabling reduced rework, shorter containment windows, and protected profit margins.
How cloud MES differs from on-premises MES systems
The main difference between cloud MES and on-premises MES systems is who manages the ongoing operational burden for server management, platform updates, and multi-site scaling. Cloud MES transfers platform maintenance to the cloud provider, standardizing how systems deploy across facilities.
In our deployment experience, on-premises rollouts often force teams to procure new hardware, build separate software instances, and manage independent patch cycles for every new plant. Cloud MES reduces multi-plant infrastructure overhead by providing a shared platform that enables repeatable deployment templates.
While cloud systems require reliable network connectivity, on-premises setups frequently suffer from version drift, delayed security patches, and inconsistent compliance practices across plants. Selecting the right model depends on your operational constraints rather than abstract software comparisons.
| Architectural Topic | What You Manage Most With Cloud MES | What You Manage Most With On-Premises |
| Upgrades and Patches | Focus on change control and validation windows rather than hardware maintenance. | Own manual patching, downtime scheduling, and version support. |
| Multi-plant Consistency | Reuse standardized templates to keep execution rules aligned across sites. | Manage instance drift and site-specific custom code variations. |
| Scaling New Lines | Add stations and operators without sizing new local server hardware. | Procure and configure local IT infrastructure for every capacity expansion. |
| Connectivity Planning | Design resilient edge buffering to maintain shop floor continuity. | Rely primarily on local plant network health inside the facility boundary. |
| Security Operations | Manage user roles, identity, and audit trails within a unified platform. | Manage physical server access, operating system hardening, and local backups. |
| Cost Structure | Budget for subscription services and active operational configuration work. | Budget for capital hardware purchases, internal support, and refresh cycles. |
Core capabilities to require in cloud manufacturing software
Core capabilities required in cloud manufacturing software include controlled routing, unit-level serialization, closed-loop defect logging, electronic work instructions, and multi-site reporting. Without these foundational controls, a system provides reporting dashboards without real execution enforcement.
We see operations encounter friction when quality checks are corrected after the fact rather than enforced during transaction time. Controlled routing prevents process drift from becoming scrap by enforcing mandatory signoffs at execution time.
Key capabilities to mandate during evaluation include:
- Controlled Routing: Enforces correct operation sequencing and captures required digital signoffs before a unit advances.
- Unit-level Serialization: Links component lot numbers, process steps, and test parameters to individual product history.
- Closed-loop Defect Logging: Captures nonconformances and forces structured repair workflows before product release.
- Electronic Work Instructions: Delivers version-controlled visual assembly guidance directly to workstation screens.
- Multi-site Reporting: Compares global line performance using standardized data schemas and identical time metrics.
Data, integration, and latency considerations for shop floor control
Shop floor control depends on sub-second transaction timing, resilient edge buffering, and clean system ownership boundaries. In our deployment experience, cloud MES functions best when production events serve as the real-time source of truth for plant activity.
Consider a packaging line scanning serialized barcodes at final inspection to validate work orders, routing steps, and label compliance prior to shipment. If every scan waits on round-trip network calls to external databases, line stalls occur and operators resort to undocumented workarounds.
Edge buffering allows local stations to process scans immediately while synchronizing supporting data asynchronously to prevent line stalls.
Keep enterprise integrations tightly focused. The ERP system supplies work orders, bill of materials revisions, and inventory contexts, while the MES manages step-by-step execution and component genealogy.
Hardware integrations should start with critical quality signals before expanding to secondary telemetry. Clean master data governance prevents broken reports even when interface calls succeed. This integration architecture reflects our guidelines for Connected Manufacturing.
Security, compliance, and residency needs for regulated manufacturers
Regulated manufacturing requires enterprise-grade security controls that verify user identity, maintain immutable audit trails, and enforce data residency policies. Security audits fail more frequently from human process gaps than from cloud infrastructure vulnerabilities.
Industry research indicates that 68% of breaches involve a human element, such as shared user accounts or overbroad permissions. Role-based access controls support FDA and ISO compliance by restricting operator permissions strictly to active station tasks.
Cloud MES platforms support regulatory compliance controls (such as FDA 21 CFR Part 11 and ISO 13485 requirements) by managing system access and logging event history. Operators should access only the specific screens required for their shift, while engineering updates follow formal digital approval paths.
Verify encryption standards, key management protocols, and data residency options prior to system launch.
Implementation steps to scale from pilot to multi-plant rollout
Scaling cloud MES requires validating a repeatable operational template on a single pilot line before replicating the standard across additional facilities. A pilot deployment should validate core routing rules, operator data capture, and critical system integrations on a defined product family.
In our multi-site deployments, scaling fails when plant governance is treated as optional. Using a successful pilot line as an enterprise reference model enables rapid multi-plant scaling with controlled local variation.
Replicating an established template avoids full-scale simultaneous deployments that overwhelm project resources. Platforms like 42Q enable teams to establish a baseline configuration on line one and deploy it across additional lines and plants with standardized master data.
Training should focus specifically on handling process exceptions to prevent teams from returning to paper records.
Common failure modes when moving MES to the cloud
Most cloud MES failure modes originate from unaddressed shop floor process variation, messy master data, and weak integration boundaries rather than cloud technology limitations. Moving messy legacy processes to the cloud accelerates the visibility of operational gaps without fixing the underlying execution habits.
We see teams struggle when attempting to write custom software logic to match every unapproved shift habit. Treating cloud MES as an operating system model with strict data governance eliminates silent release risks and reporting arguments.
Avoid common deployment traps by establishing clear data ownership across systems:
- Over-customization: Writing custom software code to mimic legacy habits creates brittle installations that stall future updates.
- Vague Data Boundaries: Allowing ERP, MES, and local controllers to claim ownership of the same data fields causes reporting disputes.
- Permissive Role Design: Granting broad system access during launch erodes audit readiness and increases bad release risks.
- Neglected Network Planning: Failing to plan for edge buffering causes latency stalls that encourage operators to bypass the system.
Sustained manufacturing value comes from pairing cloud software with disciplined process ownership and master data control. Enterprise platforms like 42Q provide the architecture and templates necessary to support consistent, scalable execution across global factories.
Ready to evaluate cloud MES for your manufacturing footprint?
Request our Cloud MES Architecture & Compliance Audit Checklist to evaluate your multi-plant readiness and schedule a demo to see how 42Q controls execution across global plants.
Key Takeaways
- Standardize the Operating Model: Cloud MES scales only when you standardize execution rules, master data ownership, and plant-to-plant governance before expanding to new sites.
- Enforce Core Shop Floor Controls: True production value comes from strict route enforcement, unit-level genealogy, closed-loop defect logging, and controlled work instructions with sub-second transaction timing.
- Design for Compliance Early: Security controls, role-based access, audit trails, and data residency must be treated as core production requirements from day one of deployment.
Why Multi-Tenant Cloud Architecture Changes MES Outcomes
Why Multi-Tenant Cloud Architecture Changes MES Outcomes
Multi-tenant cloud MES architecture directly dictates how fast an enterprise can scale lines and how steadily plants run daily operations. In our deployment experience, MES projects stall not because of shop floor software features, but because platform architecture quietly sets structural limits on what execution can achieve across sites.
Cloud adoption is now an operational baseline rather than a niche move. Eurostat reports that 45.2% of EU enterprises purchased cloud computing services in 2023. Choosing a multi-tenant cloud MES architecture shifts plant-level server management overhead into standardized, enterprise-grade capabilities.
This connects directly to the metrics explored in our MES Business Case guides, where speed to value and total cost of ownership depend heavily on avoiding isolated site infrastructure.
Multi-tenant cloud MES architecture shapes cost, speed, and control
Multi-tenant cloud MES architecture runs multiple facilities on a single, logically separated software stack to lower operational costs and accelerate software updates across plants. In our deployment experience, this model shifts engineering effort away from hardware maintenance and toward active process control.
A multi-tenant architecture shifts upgrade management, platform security, and backend scalability to the vendor while providing consistent cross-plant governance. We see customers struggle when trying to scale single-tenant or legacy on-prem systems across multiple plants because every site requires separate server management and custom software patches.
Multi-tenant design proves essential when supporting multiple facilities, diverse product lines, or strict regulatory requirements. You trade low-level server configuration control for enterprise standardization. This structural shift supports enterprise-grade security standards and simplifies global compliance audits across facilities.
Seven ways multi-tenant cloud MES architecture improves MES scalability
Multi-tenant cloud architecture improves MES scalability by centralizing core platform services, enabling rapid site onboarding without custom code forks. Scalability covers how cleanly you launch new sites, how quickly you adapt shop floor workflows, and how stable integrations stay after routine platform updates.
1 Shared platform services reduce infrastructure work for each plant
Shared platform services handle logging, user authentication, monitoring, and database operations centrally so plant IT teams do not rebuild infrastructure at every site. Centralizing core platform services removes duplicate setup work and drastically reduces server management overhead for local IT and OT teams.
This standardized foundation makes line performance and system reliability easy to compare across facilities. Plant teams align on global platform standards rather than maintaining custom local server configurations.
2 Elastic compute and storage handle peak production without redesign
Elastic cloud capacity expands compute power and data storage automatically during high-volume production cycles without requiring local hardware refreshes. In our deployment experience, end-of-quarter output spikes can easily push traditional on-prem servers to their processing limits.
Elastic compute resources absorb sudden production volume spikes and scale back automatically when line volume normalizes. This elasticity protects shop floor performance when additional shifts and high test-data volumes hit the system. Systems establish clear performance guardrails to ensure heavy workloads do not impact adjacent line operations.
3 Unified data model supports cross-site reporting and benchmarking
A unified data model standardizes event structures and operational definitions so key performance indicators remain identical across all manufacturing facilities. Standardized data schemas enable real-time yield and cycle-time visibility across global plants without manual spreadsheet reconciliation.
We see engineering teams resolve root cause defects faster when defect taxonomy and unit histories match across factories. Clean master data governance enables meaningful plant-to-plant benchmarking. This structural consistency links directly to our guide on Connected Manufacturing Architecture across multi-site enterprises.
4 Continuous updates deliver fixes and features with less disruption
Continuous cloud updates deliver software improvements and security patches on a predictable schedule to avoid costly multi-year software upgrades. Delivering frequent, incremental cloud updates eliminates the risky full-scale simultaneous deployment projects that frequently stall MES progress.
Software defects carry severe financial risks on the floor. Inadequate software testing is estimated to cost the US economy $59.5 billion per year, particularly when complex enterprise integrations and regulatory controls are involved. Regulated plants use disciplined change control and validation planning to keep continuous cloud releases predictable and auditable.
5 Central security controls simplify access, audit trails, and compliance
Centralized security management applies uniform role-based access, password governance, and audit logging across every connected plant. Standardizing access controls centrally eliminates local security exceptions that compromise compliance audits.
This model streamlines user onboarding when technicians move between shifts, lines, or production plants. Central security management supports compliance controls for regulatory frameworks without requiring local site customization. Teams maintain formal segregation of duties reviews to verify audit event completeness.
6 Configurable workflows keep local process needs without code forks
Configurable workflow engines allow plant teams to adapt routes, quality gates, and work instructions without altering core platform source code. Separating site-specific configuration from core software code prevents custom code forks that complicate platform updates.
We see customers struggle when local engineering teams write custom code modifications that break during routine platform updates. Governed workflow configurations preserve local process flexibility while protecting long-term software maintainability.
7 Standard APIs speed integrations across ERP, PLM, and equipment
Standardized application programming interfaces establish reusable interface contracts that connect shop floor equipment, ERP systems, and PLM software. Using standard APIs enables fast, repeatable system integrations across ERP work orders, PLM revisions, and shop floor test stations.
A cloud platform like 42Q operationalizes this integration model through pre-built connectors that scale across plants with minimal rework. Defining clear data ownership for interface mappings prevents data translation errors between shop floor systems and enterprise planning records.
| What You Scale | What to Expect From the Architecture |
| 1 Shared platform services reduce infrastructure work for each plant | You reduce repeated IT setup and focus more on process control. |
| 2 Elastic compute and storage handle peak production without redesign | Peak loads absorb better when resource limits are clearly defined. |
| 3 Unified data model supports cross site reporting and benchmarking | Cross-plant metrics align when events and definitions stay consistent. |
| 4 Continuous updates deliver fixes and features with less disruption | Smaller releases reduce upgrade shock when validation is planned. |
| 5 Central security controls simplify access, audit trails, and compliance | Access rules and audit logs standardize across plants with less drift. |
| 6 Configurable workflows keep local process needs without code forks | Local variation stays manageable when configuration stays governed. |
| 7 Standard APIs speed integrations across ERP, PLM, and equipment | Integrations repeat cleanly when interfaces follow one contract. |
Key questions to compare multi-tenant and single tenant MES
Evaluating multi-tenant versus single-tenant MES requires determining which organization carries the ongoing operational burden for software maintenance, platform scaling, and shared infrastructure. Multi-tenant architectures transfer server management, security patching, and core platform scaling to the software vendor. Single-tenant architectures provide total environment isolation and local control over upgrade timing.
The right tenant architecture depends on non-negotiable operational boundaries, including validation cadence, integration stability, and isolation requirements. In our deployment experience, a multi-tenant fit becomes clear when enterprise leadership prioritizes network-wide repeatability over isolated plant customization.
Before finalizing an architectural decision, leadership teams should evaluate these core operational questions:
- How frequently will your plants require validated change control reviews?
- How much site-to-site process variation will your engineering standards allow?
- Which enterprise integrations must remain stable during routine platform updates?
- What specific uptime targets and peak throughput volumes must the system support?
- Which enterprise team owns identity management, audit trails, and user access reviews?
Multi-tenancy delivers maximum value when configuration governance is strict and master data is managed as a shared enterprise asset. Single-tenant environments fit niche facilities where complete isolation outweighs the higher cost of separate software stacks. Operations running 42Q in multi-tenant mode treat rollout as a strategic operating model change with defined owners for data schemas, workflow rules, and interface boundaries.
Ready to evaluate the right cloud MES architecture for your plants?
Request our Multi-Tenant Governance Audit Checklist to benchmark your platform readiness, or schedule an architecture demo to see how 42Q simplifies multi-site deployments.
Key Takeaways
- Shift Platform Infrastructure: Multi-tenant cloud MES architecture shifts scalability from plant-level hardware work to platform-level standards, accelerating rollout speed and cross-site consistency when configuration governance is tight.
- Reduce Upgrade Shock: Shared services and continuous updates minimize multi-year upgrade projects and security drift, while disciplined change control keeps releases predictable for regulated operations.
- Evaluate Core Non-Negotiables: The right tenant model depends on strict operational requirements such as validation cadence, integration stability, and isolation needs rather than simple feature lists.
Connected Manufacturing Architecture for Modern Factories
Connected Manufacturing Architecture for Modern Factories
In our deployment experience, a connected manufacturing architecture turns raw machine data into specific actions your teams can trust. Shop floor connectivity often fails when deployments start with a mandate to capture all data rather than focusing on supporting specific workflows with strict operational constraints.
A factory network that exposes machines without strong identity and segmentation raises enterprise risk. This risk is highly tangible, as reported losses from internet crime reached $12.5B in 2023. Connected manufacturing works when you design the architecture around context, timing, and control rather than just building more reporting dashboards.
Data must arrive with the precise meaning that operators and enterprise systems need to function properly. It must arrive reliably when the line is running and buffer safely when the network drops. The practical goal is to connect equipment to improve quality and traceability without creating an unsustainable hardware maintenance burden.
Connected manufacturing links machines, people, and systems with data
Connected manufacturing serves as an operating model where shop floor events flow into business systems with enough context to trigger consistent actions. It links equipment signals to work orders, product identity, routing, and quality rules. It also connects floor staff to these same facts through real-time alerts and digital work instructions.
The true value of this architecture comes from closed execution loops rather than raw data volume. Useful connectivity starts when a machine event answers a specific operational question. A system should ask if a torque driver registered 4.5 Nm for a specific serial number rather than just pushing every data tag to a cloud database.
This discipline keeps network loads predictable, lowers storage costs, and prevents arguments over reporting accuracy. It also establishes a clear boundary between passive monitoring and active control. Treating connectivity as a control problem naturally prioritizes time synchronization and operator workflows over one-time integration tasks.
Map shop floor data flows before selecting connectivity tools
Mapping shop floor data flows requires defining the exact decisions the data supports before evaluating any software or hardware. You need to know which events require sub-second latency, which can be delayed, and which must remain on-premises. That map defines the minimum dataset, the required timing, and the systems of record.
A practical map ties each data flow to a specific business object and an operational owner. The same temperature reading can function as a maintenance signal or an FDA compliance record depending on context. Without explicit data ownership, teams build parallel pipelines and spend months reconciling mismatched timestamps and part identifiers.
To ensure data mapping is effective, we recommend building definitions around these core checkpoints:
- Define the action each event should trigger and assign a clear owner.
- Specify latency targets in actual seconds rather than using vague marketing terms.
- Set data quality rules for units of measure, acceptable ranges, and missing values.
- Decide retention and audit requirements before finalizing cloud storage configurations.
- Document exactly where each identifier originates to maintain system authority.
This mapping step reveals constraints that heavily shape your architecture. Some lines need deterministic timing for interlocks, while others only need periodic status updates. A clean map prevents expensive rework when IT security reviews or validation requirements arrive late in the deployment.
Choose an architecture that fits edge, cloud, and latency needs
Selecting the right architecture requires splitting responsibilities across the edge and the cloud based on strict latency and reliability targets. The edge handles local collection, buffering, and basic normalization physically close to the equipment. The cloud manages cross-plant visibility, analytics, and integration with broader enterprise systems.
The correct architectural split is the one your specific team can operate with predictable support and clear ownership. Start the design process by mapping failure modes instead of just comparing feature lists. Your design must assume network links will drop and machines will reboot mid-shift to prevent critical gaps in traceability records.
| Architecture Checkpoint | What to Standardize Early | What Breaks When Ignored |
| Latency Targets | Event timing budget from sensor to action | Alerts arrive too late to stop scrap |
| Offline Behavior | Edge buffering and replay rules | Gaps appear in traceability records |
| Time Alignment | Shared time source and timestamp format | Cycle time and genealogy cannot reconcile |
| Data Contract Ownership | Versioned schemas and change control | Dashboards drift and integrations fail silently |
| Security Boundary | Segmentation and identity for every connector | One compromised node spreads laterally |
We see most modern factories land on a hybrid pattern to balance these needs. Collection and immediate responses stay close to the line, while aggregated records flow upward. Operators get fast, local feedback while executives get comparable metrics across global plants.
Integrate manufacturing equipment using protocols, gateways, and adapters
Integrating manufacturing equipment successfully requires separating physical device connectivity from the semantic meaning of the data. Adapters handle device-specific communication and expose a normalized event stream. Gateways manage edge buffering, basic validation, and secure data forwarding.
Downstream systems handle the business context so equipment upgrades do not force a complete redesign of enterprise reporting. By separating the physical connection from the data context, quality and traceability stay consistent even if a physical device is replaced.
Consider a concrete pattern for a new production line. A torque tool and a vision inspection station each send results to an edge gateway. The gateway stamps the time, validates the ranges, and publishes a common event with a unit ID and a pass or fail status. The MES then links that event to the current work order and routing step.
Device integrations frequently present challenges because vendors expose different data and naming conventions vary wildly. Your gateway layer should insulate the rest of the enterprise software stack from those hardware differences. Plan operational details early, as a gateway that cannot be patched safely becomes a permanent enterprise risk.
Use MES and context models to make data usable
MES and context models append routing steps, operator IDs, and material lots to raw shop floor signals to create auditable records. Without that applied context, you have connectivity but you lack actionable connected manufacturing. Context is what makes data comparable across different lines and global plants.
Interoperability gaps carry a very real cost in asset-heavy operations. Inadequate interoperability in the U.S. capital facilities industry was estimated at $15.8B per year. Connecting machine context to a central system eliminates duplicated integrations, manual reconciliations, and brittle reporting definitions.
This integration strategy ties directly into the ROI outlined in our MES Business Case models. A cloud MES such as 42Q serves as a practical anchor for this architecture. It already models the routing, serialization, and defect loops that raw device data simply cannot express.
Secure and scale connectivity across lines, plants, and suppliers
Securing cross-plant connectivity requires treating every machine connector as a managed identity with strict least-privilege access. Segmentation keeps machine networks isolated from business networks. Authenticated endpoints prevent unknown devices from joining the environment silently.
Logging and audit trails make rapid investigations possible without stopping production to guess what happened on the floor. Scaling multi-plant connectivity relies on treating security as a repeatable deployment pattern rather than a custom project for every single line.
Start with the access paths that your hardware maintenance teams already use. Remote access should be brokered, time-bound, and fully recorded. Default passwords must be removed before any connector is commissioned on the floor. You must establish strict patch windows and rollback plans for edge nodes.
Scaling across plants also introduces enterprise governance questions. Teams need shared naming rules, shared definitions for KPIs, and a single source of truth for master data. A scalable design respects export controls and keeps sensitive data local while publishing only the events needed for global traceability.
Avoid common connectivity failures in deployment and long term operations
Avoiding deployment failures requires optimizing for operational durability and data ownership rather than just quick signal capture. The fixes are highly practical. You need versioned schemas, disciplined change control, clear alarm ownership, and ongoing connector support.
Connected manufacturing becomes reliable when the core architecture remains stable during network outages, compliance audits, and line reconfigurations. Execution quality and system reliability will outlast feature breadth over the long term.
Watch closely for quiet failure modes that masquerade as progress. A dashboard that depends on manual spreadsheet corrections will inevitably collapse during peak production volume. A data model that skips units of measure and identifiers will generate shop floor arguments instead of actionable insight.
The best manufacturing teams treat shop floor connectivity as a product they actively operate rather than a one-time project. This operational mindset reflects how 42Q was built by manufacturing teams that lived with these integrations shift after shift. When you focus on context and timing, you connect equipment once and keep it useful as your business scales.
Ready to build a reliable shop floor network?
Request our Shop Floor Connectivity Architecture Checklist to audit your current edge and cloud data flows, or schedule a demo to see how 42Q centralizes machine context securely.
Key Takeaways
- Focus on Context: Define connected manufacturing around specific actions rather than raw data volume so equipment signals consistently link to work orders, quality rules, and traceability records.
- Map Before You Buy: Start shop floor connectivity with a data flow map that sets latency targets, data ownership, and versioned contracts before selecting protocols or gateways.
- Build for Durability: Use a hybrid edge and cloud architecture with buffering, time alignment, and strong segmentation so connectivity stays reliable through outages and compliance audits.
Scaling Connected Manufacturing Across Multiple Plants
Scaling Connected Manufacturing Across Multiple Plants
Multi-plant manufacturing visibility comes from shared standards and disciplined execution across sites. In our deployment experience, connected manufacturing fails at scale when each plant measures work differently. When facilities code defects differently and treat data as a local asset, teams cannot act on production signals with confidence.
About 70% of international trade involves global value chains. That economic reality makes multi-site manufacturing a management system problem first and a software selection problem second.
Treating MES deployment as a continuous capability targets stable adoption and protects enterprise data integrity. This connects directly to the ROI discussed in our MES Business Case guides, as downstream analytics and compliance rely entirely on clean, unified data.
Clarify how multi-site manufacturing should be managed centrally
Central management must set non-negotiable rules for data, process, and accountability while leaving room for local execution. You need one operating model that defines who owns standards, who approves exceptions, and how issues escalate across plants.
Global visibility only matters when a specific owner is accountable for acting on the data across facilities. Otherwise, delays in containment, inconsistent release decisions, and conflicting quality interpretations begin to affect customer commitments and margin performance. Local autonomy still exists, but it happens inside clear guardrails.
Start with a simple question you can answer in one sentence. What decisions must be made the exact same way everywhere? Typical answers include release-to-production criteria, traceability requirements, and quality holds.
Keep this list short, then assign owners who are accountable for maintaining those standards across engineering, quality, and operations. We see customers struggle when ownership is vague because each plant will interpret "standard" as "close enough," causing data to drift. A single escalation path for systemic defects and a shared approach to temporary deviations will do more for visibility than another reporting dashboard.
Standardize work definitions, routing, and quality rules across plants
Standardization requires making terms like a step, a pass, a fail, and a rework mean the exact same thing across every facility. Routing should control the sequence and required checks at execution time rather than just documenting intent. Quality rules must be executable so the same defect code triggers the same containment action everywhere.
A step, a pass, a fail, and a rework must have identical meanings across every plant to maintain data integrity. Keep your standards practical. A global routing library can support local variants, but only if the base route and required checkpoints remain common.
Electronic work instructions should be written for the operator’s moment of need, with clear revision control and proof of acknowledgment. Inspection plans should tie to the same measurement definitions and sampling logic.
This enables plant-to-plant comparisons to hold up under scrutiny. Tradeoffs will show up quickly in any multi-site deployment. Standardize what must happen globally, then let sites decide how it happens through tooling and staffing.
Design data governance for traceability, genealogy, and master data
Data governance defines the minimum record you must trust across every plant, every product, and every shift. Traceability must link materials, process steps, test results, and disposition into one unbroken chain of evidence. Genealogy must survive rework, component swaps, and partial builds without losing the core product path.
Traceability records must link materials, tests, and dispositions to each unit automatically without manual stitching or spreadsheet reconciliation. Master data must stay synchronized so the same part number points to the exact same meaning globally. A good way to test your design is to walk a single serialized unit through a cross-plant scenario.
Imagine one unit starts assembly in Plant A, gets held for a test failure, ships to Plant B for repair, and returns to Plant A for final pack out. The record should show the original material lots, the exact repair actions, and the updated test results clearly.
Make governance operational rather than theoretical. Define naming standards, defect taxonomies, unit of measure rules, and time synchronization requirements. Then assign clear ownership for master data changes, plus a method to audit drift.
Select an MES setup that delivers global production visibility
An MES for global operations provides one view of production status, quality, and traceability across sites without forcing identical hardware footprints. A scalable setup provides consistent records, workflows, and reporting definitions while allowing controlled local variation. It also supports site templates so a new line or plant does not restart the design from scratch.
Plants that get the most value from connected execution treat the MES as a shared system of record rather than a localized application. Architecture choices matter in this phase. A single logical system with shared master data simplifies analytics and reduces reconciliation work.
Results can be material when execution is consistent. Several manufacturing sites highlighted by the World Economic Forum’s Global Lighthouse Network reported defect reductions of up to 90%. Those outcomes rely heavily on standard processes and data governance rather than isolated software features.
| Checkpoint | Defining benchmarks for success across plants |
| Operating Ownership | A named global owner approves standards and resolves cross-site conflicts. |
| Process Definitions | Steps, defects, rework, and holds follow the same definitions in every plant. |
| Traceability Record | Materials, tests, and dispositions link to each unit with no manual stitching. |
| Integration Boundaries | ERP stays the planning record while MES stays the execution and quality record. |
| Rollout Repeatability | A site template limits local changes and keeps reporting comparable globally. |
| Performance Cadence | Shared KPIs and escalation rules trigger action, not just reporting. |
Plan integrations for ERP, PLM, and shop floor systems
Integrations must protect a clean separation of responsibilities while keeping data flow timely and reliable. The ERP should plan and account, while the MES executes workflows and records production events. PLM manages product definitions, while the shop floor captures actuals in real time.
The primary goal of integration is to build automated checks that stop bad data before it spreads to other facilities. Start with the transaction paths that create the most risk when they break. Production orders must arrive complete and consistent.
Material consumption and component traceability must flow back with clear timestamps. Quality dispositions must update enterprise status so planning and shipping do not work from stale data. Each integration should include validation rules, retries, and active monitoring.
Silent failures create the worst kind of visibility gap. To protect integration integrity, we recommend the following steps:
- Define one owner for each data object and system of record.
- Use a consistent identifier strategy for units, lots, and work orders.
- Set latency targets for order release, consumption, and quality status.
- Build automated checks that stop bad data before it spreads.
- Monitor interfaces with alerts tied to operational escalation paths.
Scale rollout with a site template, training, and change control
Scaling works when you treat each new plant as a controlled variation of a proven baseline template. A site template should include standard workflows, role permissions, reporting definitions, and integration mappings. Change control must protect global consistency while still letting plants improve over time.
Lock the site template once it runs stable through normal shift patterns before expanding to additional facilities. Training must focus on how work is executed in the system, which ties directly back to building an effective operator training program.
Sequencing matters for a full-scale simultaneous deployment. Pick one site that represents typical complexity. After that facility is stable, expand site by site with clear entry criteria like master data readiness and supervisor training completion.
Each deployment should end with a short stabilization period where issues are triaged centrally. Expect friction from the floor and engineering, but address it with practical controls like reducing duplicate entries and setting a predictable path for urgent deviations.
Run ongoing performance reviews using shared KPIs and escalation paths
Ongoing performance management treats global MES visibility as a daily process control system instead of just a reporting layer. Shared KPIs must tie to corrective actions that are standard across all plants, such as containment or route corrections. Escalation paths must be explicit so recurring issues do not get trapped in local workarounds.
Review a small set of vital KPIs on a fixed cadence with the exact same definitions to enforce enterprise alignment. First pass yield, cycle time adherence, top defect families, rework time, and traceability completeness usually cover the essentials.
Require each plant to show the corrective action and the verification method. When a KPI moves, the response should be predictable so teams trust the system and stop debating the numbers. Connected manufacturing becomes sustainable when you protect consistency as a daily habit.
Tools matter, but discipline matters more. Every exception becomes tomorrow’s normal unless someone actively closes the loop. When execution discipline is strong, a cloud platform like 42Q becomes a shared system of record that supports cross-site alignment and strengthens leadership visibility into revenue, quality exposure, and delivery performance.
Ready to scale your production standards securely?
Request our Multi-Site MES Governance Checklist to map out your rollout strategy, or schedule a 5-minute demo to see how 42Q centralizes master data across your global plants.
Key Takeaways
- Centralize Management: Multi-plant manufacturing visibility depends on shared definitions, clear ownership, and controlled exception management rather than just adding more dashboards.
- Standardize the Data: Global MES visibility works when routing, quality rules, and traceability records stay consistent across sites through strict data governance.
- Control the Rollout: Multi-site manufacturing scales faster with a locked site template, tight ERP and PLM integration boundaries, and a steady KPI cadence with clear escalation paths.
